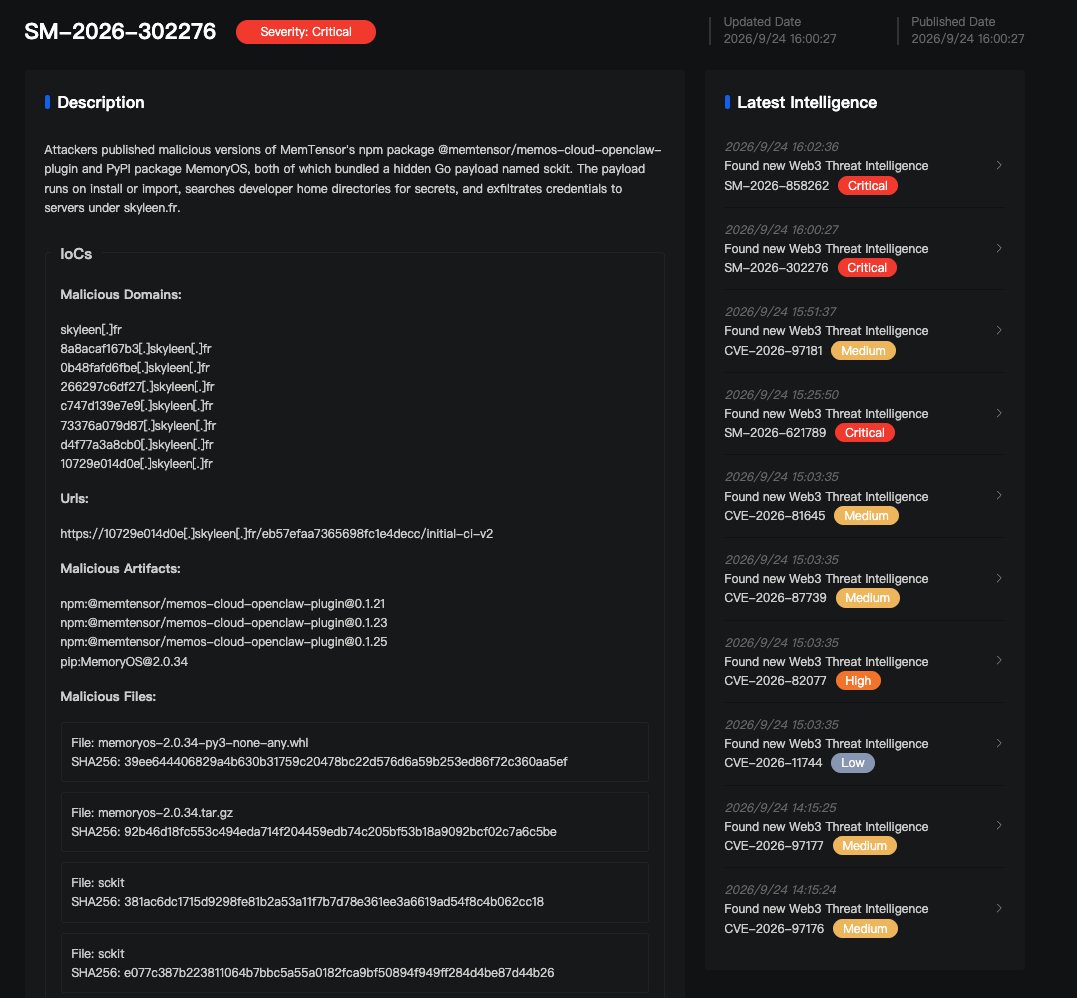
MemTensor's AI memory tooling has been compromised: MemoryOS (PyPI), the company's…
This is a dev post classified by Jev as Security (news), kept by the Dev Radar because it carries real work, not commentary.
🚨 SlowMist TI Alert 🚨 MemTensor's AI memory tooling has been compromised: MemoryOS (PyPI), the company's open-source long-term memory library for LLM and AI agents, and memtensor/memos-cloud-openclaw-plugin (npm), the official plugin connecting it to the OpenClaw agent runtime. Affected versions bundle cross-platform Go binaries that execute when the package is loaded or imported: MemoryOS==2.0.34 on PyPI, and plugin versions 0.1.21, 0.1.23 and 0.1.25 on npm. You are affected if the PyPI version has been imported in your environment, or if the npm plugin is installed and the OpenClaw gateway
Posted by SlowMist (89.9k followers) 17 h ago · 2 likes · 907 views · view the original post on X. Kept by the Dev Radar as Security. Tools mentioned: MistEye.
More dev work like this
- Installs over 750 open-source intelligence and security tools across 50 categories using… — @tom_doerr
- Shipped a new version of masker & masker-mini, improved strict F1 across all languages,… — @nickvernij
- Security is a stack. — @navi_protocol
- Private cloud environments need end to end security protection covering hosts,… — @tencentcloud
- Showboat is a Linux post-exploitation framework built for stealth and long-term access. — @PicusSecurity
- Auto-discovers devices using nmap and organizes them into labeled groups via a… — @tom_doerr
- AI security checks shouldn’t turn an unknown into a pass. — @DanKornas
- Azure security gets complicated fast. — @AiswaryaVenkit1
Every post is read and classified by Jev (TypeSafe): what it is, which market it belongs to, and whether the link is a real tool. 23.4k posts from 5k X accounts over the last 21 days, 2.7k tools, 12 markets. Collected every 5 minutes, fully re-ranked every hour — last update 2026-09-24 10:22 UTC. Full method.