What happens when autonomous pentesting goes up against a production web app that’s…
This is a dev post classified by Jev as Security (a launch), kept by the Dev Radar because it carries real work, not commentary.
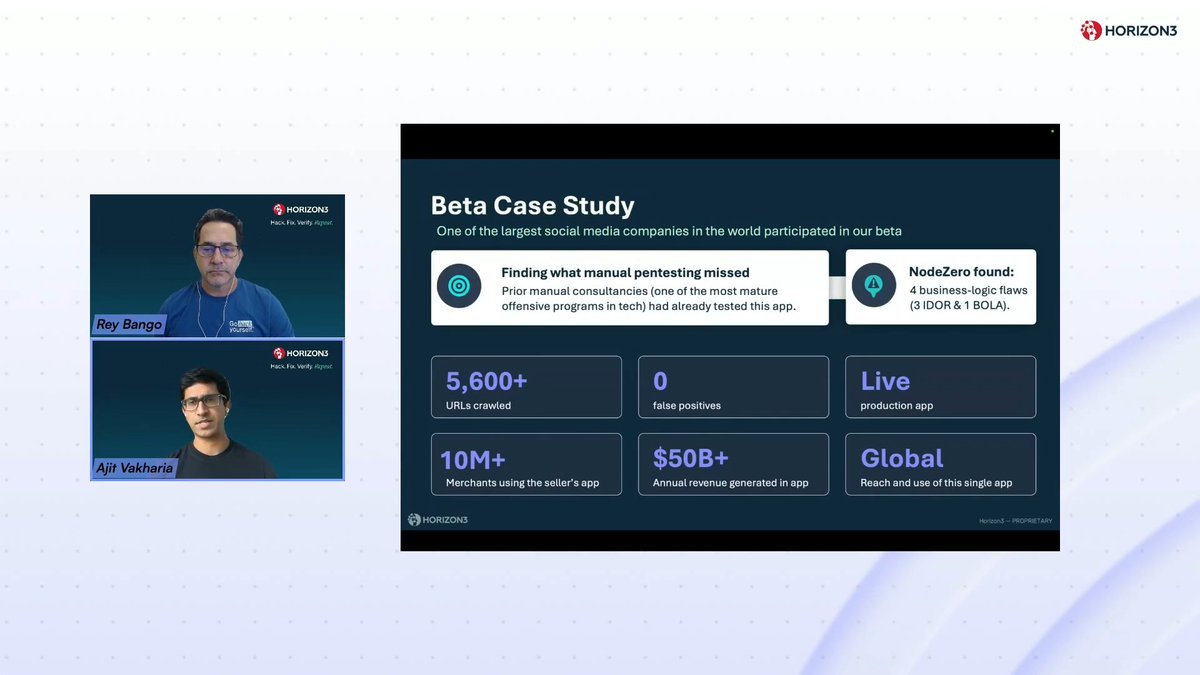
What happens when autonomous pentesting goes up against a production web app that’s already been tested manually? #NodeZero WebApp crawled 5,600+ URLs and uncovered four business-logic flaws that had been missed — with replayable proof and zero false positives. That’s the difference between scanning for potential issues and proving what attackers can actually exploit. 🔗 Watch the full on-demand webinar to see how NodeZero WebApp brings production-safe autonomous pentesting to custom web applications — and how it fits into the broader attack path across identities, infrastructure, and cloud:
Posted by Horizon3.ai (3k followers) 2 days ago · 3 likes · 155 views · view the original post on X. Kept by the Dev Radar as Security.
More dev work like this
- Wow, these slides are fantastic to just read through and contemplate. 😍… — @zooko
- How hackers use SQL Injection to compromise a website — @Hamzaonchain
- Dostlar selamlar, globaldeki en büyük Cybersecurity SFT finetuning datasetlerinden olan… — @AlicanKiraz0
- Cloudflare 团队把其内部找漏洞的那套方法做成了一个 Skill,叫 security-audit,并开源了。 — @GitHub_Daily
- Scans emails and usernames across 715+ platforms to map digital footprints and verify… — @tom_doerr
- DeepTeam runs locally to simulate attacks and uncover vulnerabilities in LLM systems. — @tom_doerr
- You can run a Uncensored 8B-cybersecurity locally on Q2_K (3.2 GB) laptop. for pentest… — @0x0SojalSec
- Software now writes and runs software: — @jfrog
Every post is read and classified by Jev (TypeSafe): what it is, which market it belongs to, and whether the link is a real tool. 13.5k posts from 4.7k X accounts over the last 21 days, 1.5k tools, 12 markets. Collected every 5 minutes, fully re-ranked every hour — last update 2026-09-19 19:24 UTC. Full method.